User Access Control and Security: Managing Access, Permissions, and Database Security
Explore essential strategies for managing user access, permissions, and database security. From authentication and authorization to encryption and regular audits, learn how to safeguard your data's integrity and confidentiality.

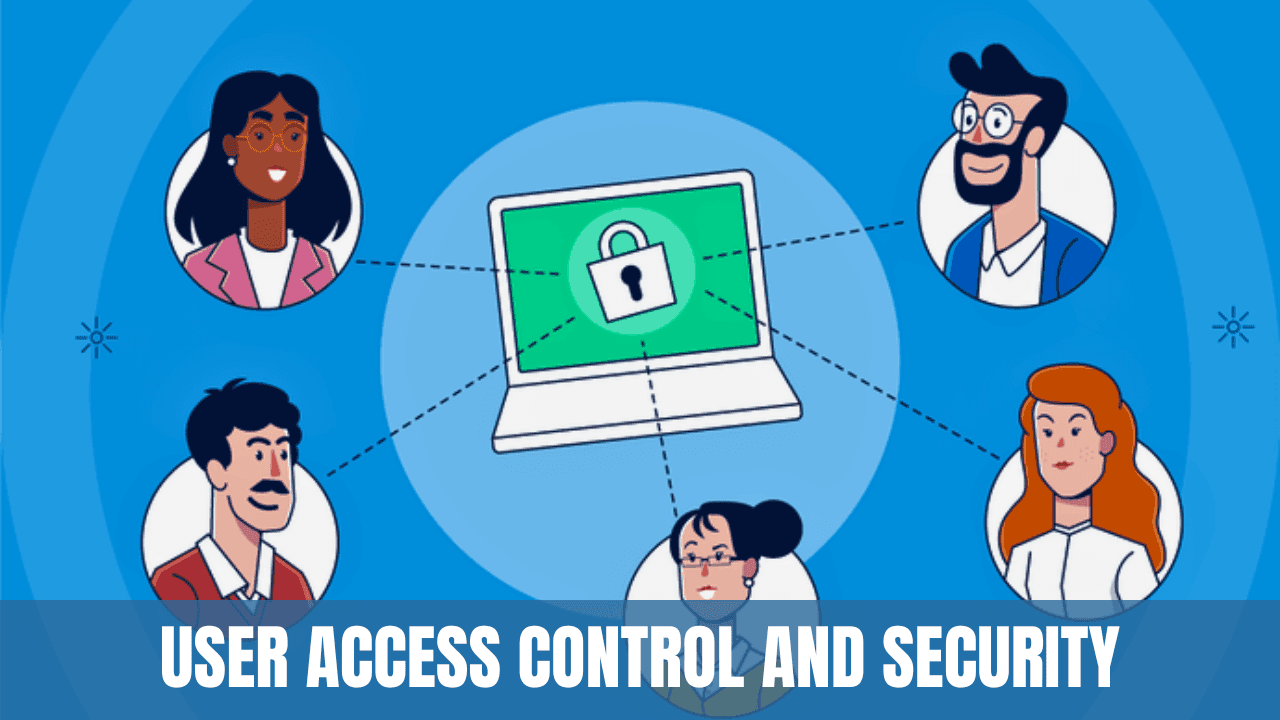
In the intricate landscape of database management, user access control and security stand as crucial components. These aspects safeguard sensitive data, ensuring that only authorized individuals have access while maintaining the integrity and confidentiality of information. This article explores various strategies for managing user access, permissions, and overall database security.
I. User Access Control
User access control is the practice of defining who has access to the database and what they can do once they access it. Key elements include:
- Authentication: Verifying the identity of users through passwords, tokens, or other means to ensure that they are who they claim to be.
- Authorization: Assigning specific permissions to users based on their roles and responsibilities within the organization.
- Role-Based Access Control (RBAC): Structuring permissions around roles rather than individual users, making it easier to manage access across large groups.
- Least Privilege Principle: Granting users only the permissions they absolutely need to perform their duties, minimizing potential security risks.
II. Permissions Management
Proper permissions management ensures that users can only access and modify the data necessary for their job functions. Important strategies include:
- Object-Level Permissions: Assigning permissions to specific database objects like tables, views, or procedures.
- Schema-Level Permissions: Controlling access at the schema level, providing a broader scope of control.
- Grant and Revoke Commands: Utilizing commands to grant or revoke permissions, allowing for dynamic control over user access.
- Audit Trails: Keeping logs of permission changes and access attempts to enable accountability and traceability.
III. Database Security Measures
Database security goes beyond access control and encompasses various measures to protect the integrity, confidentiality, and availability of data:
- Encryption: Encrypting data both at rest and in transit to protect it from unauthorized access.
- Firewalls and Network Security: Implementing firewalls and network security measures to block malicious traffic.
- Data Masking: Masking sensitive data so that it appears scrambled to unauthorized users.
- Regular Security Audits: Conducting periodic security audits to identify vulnerabilities and ensure compliance with regulations.
- Security Policies and Training: Establishing clear security policies and providing training to employees to foster a culture of security awareness.
IV. Best Practices
- Regular Review of Access Controls: Periodically reviewing and updating access controls to reflect changes in roles and responsibilities.
- Multi-Factor Authentication: Using multiple forms of verification to enhance authentication security.
- Monitoring and Alerting: Implementing continuous monitoring and setting up alerts for suspicious activities.
- Compliance with Regulations: Adhering to applicable legal and regulatory requirements pertaining to data security.
Conclusion
User access control and security in database management are multifaceted disciplines that require diligence and strategic planning. By understanding and implementing the strategies outlined above, organizations can foster a secure environment, minimizing risks, and ensuring that their valuable data assets remain protected. Whether it's defining access controls, managing permissions, or employing broader security measures, these practices form the foundation of a robust database security framework.

Vishal writes Trickyworld's tutorials and interview-preparation guides on programming, databases, cyber security and AI. Vishal has been shipping production software long enough to have firm opinions about Python, PHP, Node.js, and JavaScript, and to have been wrong about each of them at least once. The work has run the whole stack: Drupal and Laravel applications, React front ends, MySQL and MongoDB underneath, Redis and Memcached for the things that had to be fast, Apache Solr for the things that had to be findable. That last part turned out to matter more than anyone expected. Tune a Solr index for a season, then watch a language model confidently retrieve the wrong document, and you recognise an old problem wearing new clothes. Most of what is hard about AI systems is not the model. It is retrieval, caching, latency budgets, and deciding what the system does when the answer comes back wrong — which is work he has been doing since well before anyone called it AI engineering. He plays a lot of games, which is less a hobby disclosure than an admission of where a good share of his engineering instinct came from. Real-time systems with a frame budget. State that has to stay coherent while a player does something no designer anticipated. The permanent question of what happens when the frame cannot finish in time. Those habits carry over more directly than they have any right to. He has written several books on programming, all built on the same conviction: most technical writing is unclear because the author never decided what to leave out. More from Vishal → · Editorial policy