Abusing AWS SSM Agent as a Remote Access Trojan: Risks and Prevention
Comprehensive analysis of how the AWS SSM Agent can be abused as a Remote Access Trojan. Real-world examples and preventive measures for securing your AWS infrastructure are discussed.

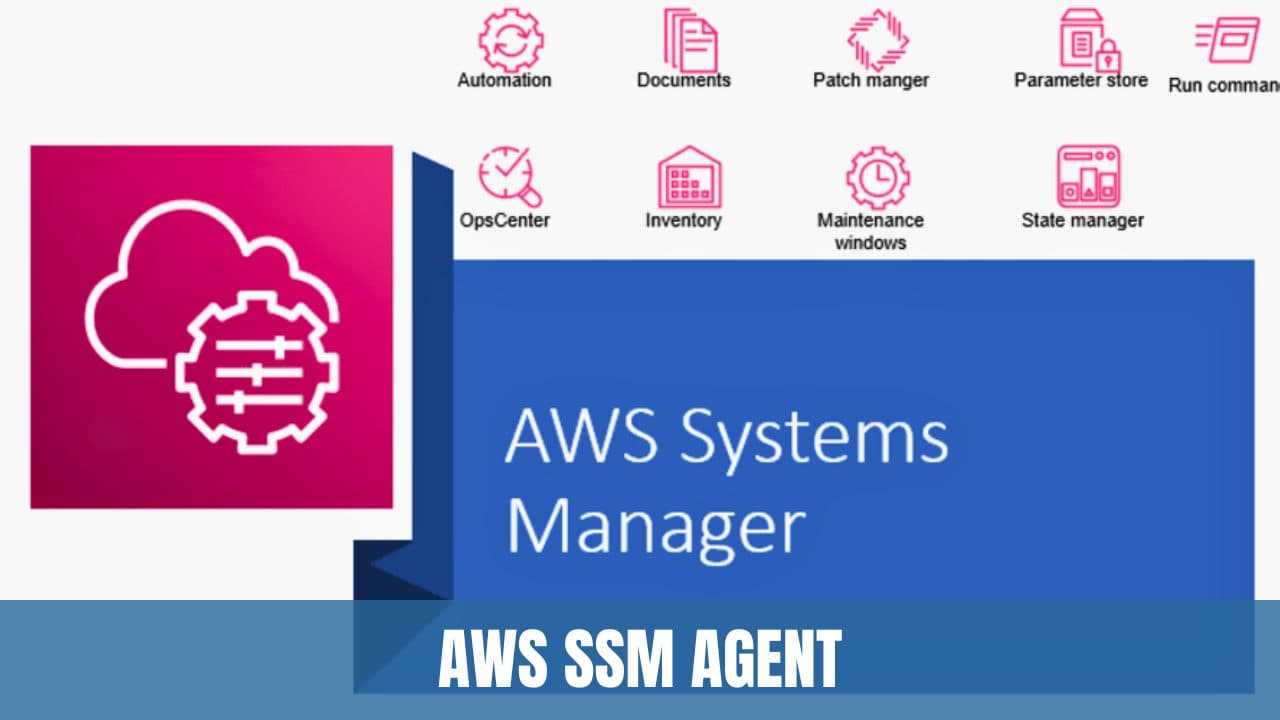
In recent times, cloud services like AWS (Amazon Web Services) have become an integral part of many organizations' IT infrastructure. AWS provides various agents and services to help manage these infrastructures. One such agent is the AWS Systems Manager Agent (SSM Agent). Although designed to facilitate centralized control over server instances, security experts have found that this very feature can be manipulated. This article aims to detail how the AWS SSM Agent can be abused as a Remote Access Trojan (RAT), along with real-world examples and preventive measures.
Understanding the AWS SSM Agent
Functions and Purposes
The AWS SSM Agent is software that resides on EC2 instances and your hybrid instances that are configured for Systems Manager. It performs functions such as inventory collection, applying patches, and executing commands from the AWS Management Console.
Vulnerabilities
Although the SSM Agent provides centralized control, this control point becomes a vulnerability if compromised. Hackers can manipulate the agent to gain unauthorized access, thereby turning it into a Remote Access Trojan (RAT).
Exploitation Techniques
Attack Vectors
The exploitation primarily involves compromising the AWS account credentials. With adequate permissions, an attacker can utilize the Systems Manager to execute arbitrary commands on the EC2 instances where the SSM Agent is installed.
Steps of the Attack
Once the AWS credentials are obtained, the attacker can then manipulate the SSM Agent to perform a range of unauthorized activities, from data extraction to system manipulation. Thus, the agent, initially meant for management, transforms into a fully functional RAT.
Real-World Examples
Case Study: Financial Company Breach of 2023
In 2023, a well-known financial company reported a security breach. Investigators later revealed that the AWS SSM Agent had been manipulated to act as a RAT. This abuse led to the compromise of sensitive customer data and caused financial repercussions for the company.
Preventive Measures
Least Privilege Principle
One of the key countermeasures against this exploitation is to apply the principle of least privilege to AWS account credentials. This ensures that even if credentials are compromised, the damage can be limited.
Multi-Factor Authentication (MFA)
Implementing MFA adds an additional layer of security. Even if the attacker obtains credentials, the MFA would act as a second line of defense.
Regular Auditing
Regularly auditing AWS logs can provide insights into any abnormal activities or access patterns, enabling quicker response in case of an incident.
Backup and Monitoring
Frequent backups and real-time monitoring can also help in quick damage control in case of any malicious activity.
Conclusion
The AWS SSM Agent, designed for efficient management of AWS services, can be turned into a RAT if not managed and secured correctly. Preventive measures like least privilege access, MFA, and regular audits can go a long way in mitigating these security risks. Awareness and constant vigilance are key in maintaining a secure cloud environment.

Vishal writes Trickyworld's tutorials and interview-preparation guides on programming, databases, cyber security and AI. Vishal has been shipping production software long enough to have firm opinions about Python, PHP, Node.js, and JavaScript, and to have been wrong about each of them at least once. The work has run the whole stack: Drupal and Laravel applications, React front ends, MySQL and MongoDB underneath, Redis and Memcached for the things that had to be fast, Apache Solr for the things that had to be findable. That last part turned out to matter more than anyone expected. Tune a Solr index for a season, then watch a language model confidently retrieve the wrong document, and you recognise an old problem wearing new clothes. Most of what is hard about AI systems is not the model. It is retrieval, caching, latency budgets, and deciding what the system does when the answer comes back wrong — which is work he has been doing since well before anyone called it AI engineering. He plays a lot of games, which is less a hobby disclosure than an admission of where a good share of his engineering instinct came from. Real-time systems with a frame budget. State that has to stay coherent while a player does something no designer anticipated. The permanent question of what happens when the frame cannot finish in time. Those habits carry over more directly than they have any right to. He has written several books on programming, all built on the same conviction: most technical writing is unclear because the author never decided what to leave out. More from Vishal → · Editorial policy